
Get started
Introduction
What Telark does, who it is for, and what it does not do.
Telark is a protection gate for your Kubernetes applications: you decide what can change an app, and when. It is a self-hosted control plane, installed with one Helm chart, that works at the level of applications instead of individual Kubernetes objects.
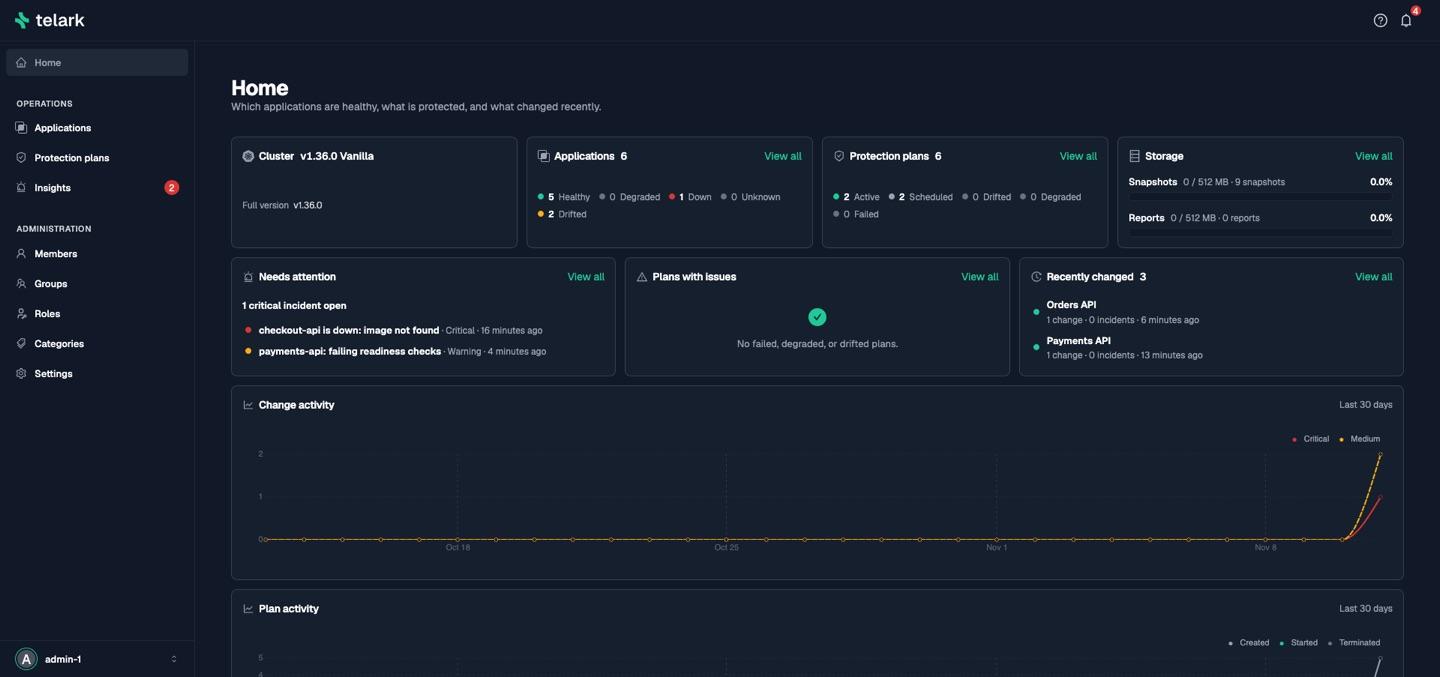
Concepts
- Applications: Telark groups workloads into applications automatically, so you protect and inspect "checkout", not seventeen Deployments.
- Protection plans: block chosen changes (deletion, scaling, image changes, config and Secret edits, storage) to an application or namespace for a time window, in weekly repeating windows, or permanently. Start in audit mode, switch to enforce when you trust what it reports. A plan can require approval; plans in the Production environment always do. Kyverno, which ships with the chart by default (or one you already run), enforces plans at admission. Telark reads the live cluster back, reports drift and every admission decision with who sent it, and writes a report when a plan or a window ends.
- Change history: every change to an application is recorded field by field, deletions included, with a snapshot you can roll back to.
- Insights: one card per affected workload with the likely cause, the evidence and the change it followed, plus a review of each application's setup against 60 rules. It is read-only, needs no API key and works air-gapped. Rules decide every finding, and a small model in your cluster only rewords it.
- Access control: passkeys or Google sign-in, roles scoped per area, and per-action deny rules such as "may edit plans, may not approve them".
Who it is for
Platform and SRE teams running shared Kubernetes clusters for several application teams, and anyone who owns release windows, maintenance windows or production freezes.
What it is not
- Not multi-cluster. One installation covers one cluster.
- Not a hosted service. You run it; the license does not allow offering it as a managed service.
- Not auto-remediation. Insights suggests; it never changes your cluster. Only a rollback you trigger writes to your workloads.
Status
Early access. Every custom resource is v1alpha1 in the telark.io API group, and the chart and API may change before 1.0. Pin a chart version. See Known limitations.