
Applications
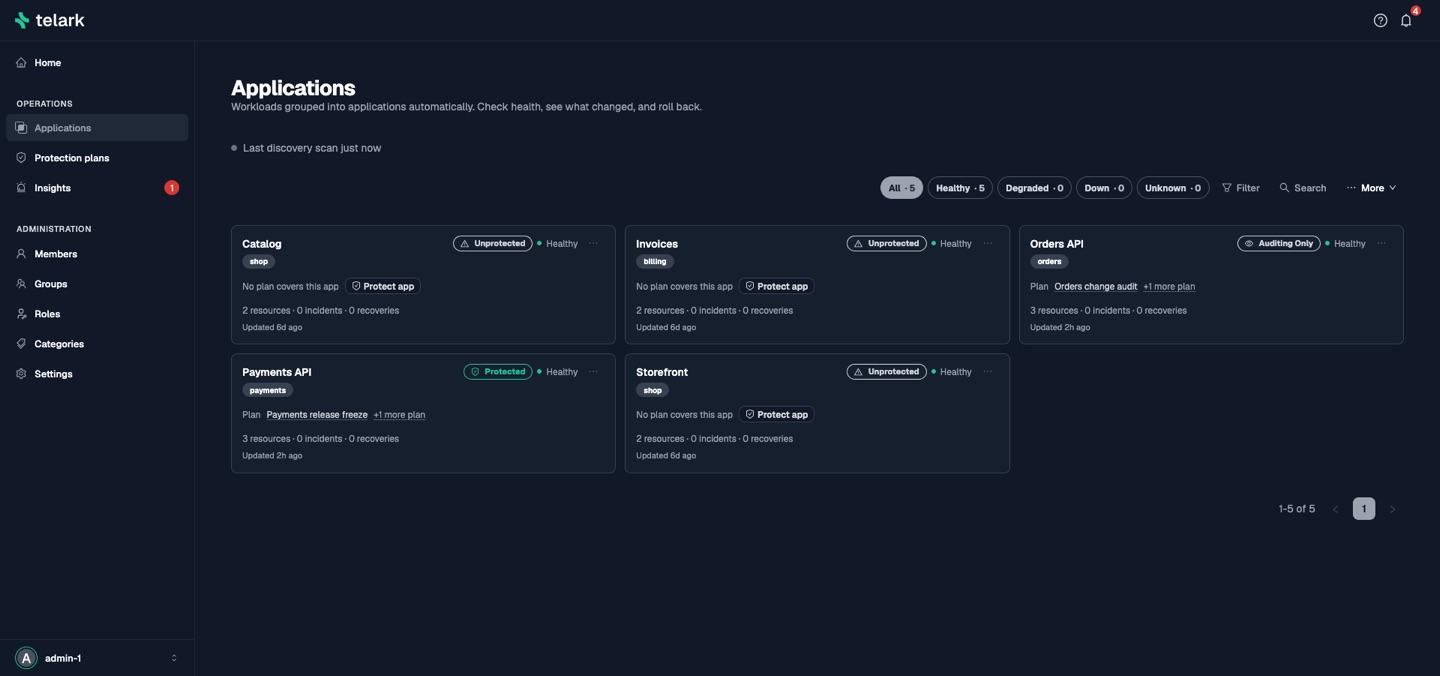
Telark groups your workloads into applications automatically, so you protect and inspect one app instead of a dozen objects.
Kubernetes has no object called "application". A service your team calls
checkout is a Deployment, a few ConfigMaps and Secrets, a Service, an
Ingress and an autoscaler, sometimes spread over several namespaces.
Protecting it or asking what changed in it object by object is slow and
easy to get wrong.
What you get
- An Applications page in the dashboard that lists every application Telark found, with its health, namespaces, workloads, images and whether it is protected.
- One unit for everything else Telark does: protection plans can scope to applications, change history and rollback are per application, and Insights are grouped by application.
- Nothing to declare. You don't create
Applicationobjects; Telark builds them from the labels your workloads already carry.
How it works
The discovery service watches these kinds in every namespace that is not excluded:
| Group | Kinds |
|---|---|
apps | Deployment, StatefulSet, DaemonSet |
batch | Job, CronJob |
| core | ConfigMap, Secret, Service, PersistentVolumeClaim, ServiceAccount |
networking.k8s.io | Ingress, NetworkPolicy |
autoscaling | HorizontalPodAutoscaler |
autoscaling.k8s.io | VerticalPodAutoscaler |
Grouping
Each resource is assigned to an application by the first label that is set, in this order:
app.kubernetes.io/nameapp.kubernetes.io/part-ofapp.kubernetes.io/componenttogether withapp.kubernetes.io/instance(a-releasesuffix on the instance is dropped)app
The label value names the application: it is lowercased and _ becomes
-. A value that is still not a valid Kubernetes object name is skipped
and logged once. The same label value in several namespaces gives one
application that spans them.
A resource without these labels joins the application of its owner (a
ReplicaSet's Deployment, for example), or else the application in the
same namespace whose name its own name contains. A ConfigMap or Secret
joins the application of the workload that references it. Jobs started by a
CronJob are folded into the CronJob, and cluster noise such as
kube-root-ca.crt, default service accounts and Helm release Secrets
is ignored.
Health
Health is derived from workload readiness: healthy, degraded,
down or unknown, with ready and total replicas. A move to degraded
or down is recorded as an incident change, and the return to
healthy as a recovery (see
Change history and rollback).
Keeping up with changes
Events are buffered per application for a few seconds, so a rollout or a multi-field edit is recorded as one change, not dozens. Discovery can run several replicas without duplicating work; see Run discovery with several replicas.
Discovery publishes each application on NATS, and the notifier persists
it as an Application resource (applications.telark.io) through the
exporter. When every workload of an application is gone, the application
is removed after two empty cycles.
Plan coverage
Each application card carries a badge for the strongest plan whose scope includes the application, directly or through one of its namespaces:
| Badge | Meaning |
|---|---|
| Protected | An active plan in Enforce mode covers it. |
| Auditing only | No active Enforce plan, but an active Audit plan covers it. |
| Not protected yet | Only scheduled or pending_approval plans cover it. |
| Not protected | No plan covers it. |
Under Protection, the card lists each covering plan as a chip:
<plan> · enforcing, <plan> · auditing or <plan> · not started.
With no plan it reads "No plan covers this app." and offers Protect,
which opens Create Protection Plan with the Applications scope, the
application selected and a name such as checkout protection. Without
the right to create plans, the button stays disabled and says why. The
application's page shows the same Protection row first in its
overview, with a link to each plan.
Failed, canceled and terminated plans don't count. Excluded kinds or resources in a plan do not remove the application from its coverage.
Excluded namespaces
Namespaces listed in spec.excludedNamespaces of the TelarkConfig
resource are not discovered, not shown on any page and refused as plan
targets. A fresh install excludes default, kube-system, kube-public
and kube-node-lease. Change the list under Settings (Contributor on
settings).
When nothing shows up
On a fresh install the Applications page reads "No applications found yet" until discovery's first pass, usually within a minute. Under Nothing showing up? it asks you to check that your workloads carry one of the grouping labels and that their namespace is not excluded, with Check again and Open discovery settings. When every application found is in an excluded namespace, the page says so.
Self-monitoring
By default Telark hides its own release namespace: the Telark services,
Redis, NATS, Ollama, Kyverno and metrics-server never show as
applications. Install with --set app.selfMonitoring.enabled=true
(discovery's SELF_MONITORING_ENABLED) to show them like any
application. While it is off, auto-cleanup removes Application resources
already created in that namespace within about two cleanup cycles. Plans
can never target the release namespace.
Force sync and reset
- Force Sync re-runs discovery for one application now
(
POST /api/v1/applications/{name}/sync). The job is queued on a Redis stream, one per application at a time, and its progress is recorded instatus.lastForceSync. - Reset deletes the application's record and snapshots and clears its
discovery state (
POST /api/v1/applications/{name}/reset). While its workloads still exist, discovery recreates it from scratch.
Limits
- Grouping is label-based. Set
app.kubernetes.io/nameon your workloads for predictable application names; a workload that carries none of the labels above, and has no owner that does, is not grouped under a name you chose. - Users can edit only an application's display name and description. Membership always follows the cluster.
- Discovery covers one cluster: the one Telark is installed in.